

When IT support depends on whoever has time, small issues linger. A license request sits unanswered, a backup check gets skipped, and a software provider’s ticket stalls because no one can find the device history. None of these is a crisis on its own. Together, they slow down billing, client work, production, and public service.
Managed IT services close that gap. The main benefits of managed IT services are improved reliability, security built in from the start, predictable budgeting, access to specialized expertise, stronger compliance readiness, and strategic technology planning. Instead of calling for help after something breaks, you work with a partner who monitors, maintains, and plans your technology every day so you can focus on your business.
A managed service provider (MSP) takes ongoing responsibility for your technology, including support, monitoring, security, backups, and planning. Unlike break-fix support, the work happens before problems interrupt your day.
Stephen Rost, director of development services at ACC Technical Services, notes: “Good managed IT services start with the business workflow, not the tool stack, because support only works when it matches how people approve work, serve clients, and manage risk.”
6 Benefits of Managed IT Services
1. Improved Reliability and Fewer Interruptions
The first change most teams notice is fewer disruptions. Proactive monitoring and scheduled maintenance catch failing drives, missed patches, and full storage before they turn into downtime. ACC Technical Services (ACC) supports clients with 99% uptime across managed environments.
Continuity matters just as much as monitoring. Say a front desk printer fails on the same morning a software provider sends an update alert. A team that knows your environment can check ticket history, confirm user access, review patch status, and verify backups before the issue spreads.
That’s why we assign dedicated teams to our managed IT services clients instead of treating every request as a one-off ticket. Your team works with people who understand your users, systems, and line-of-business applications. When a staff member leaves or a provider changes, that knowledge stays documented.
Reliable recovery is part of that stability. With tested backup and disaster recovery, shared files, email, and business records can be restored when something does go wrong.
2. Security Built In From the Start
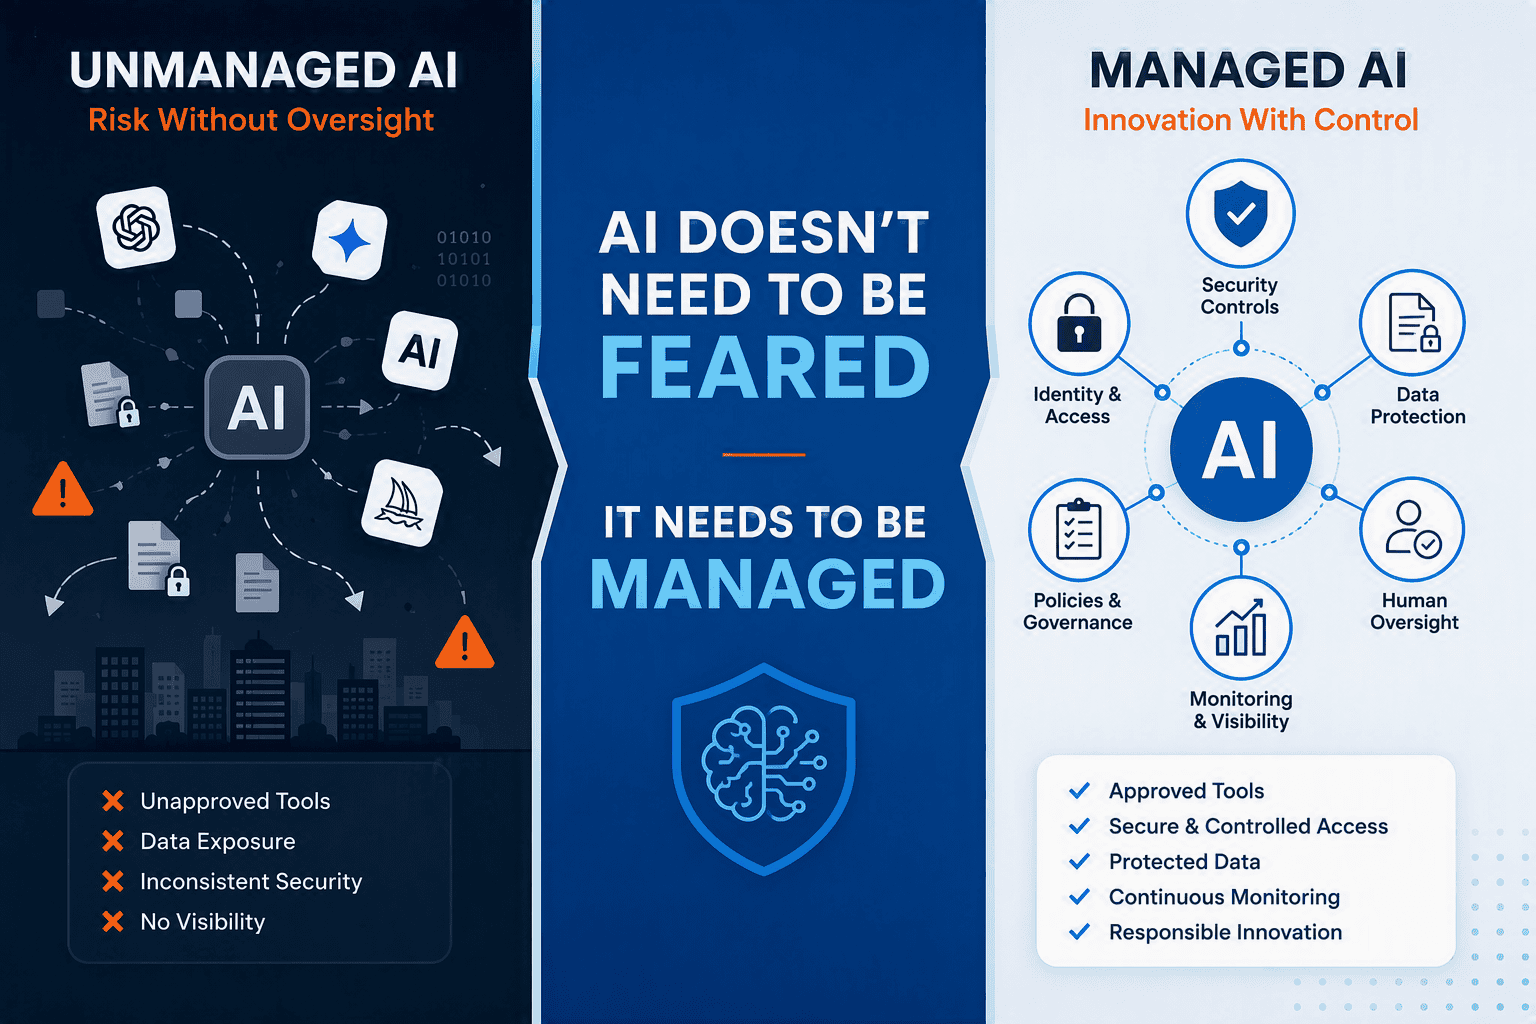
Security works best as part of every technology decision, not something added after an incident. A security-first managed IT partner layers protections across your environment:
- Continuous monitoring of laptops, servers, and accounts for unusual activity
- Scheduled, tracked patching so updates are approved and reported
- Vulnerability management that turns scan results into prioritized fixes
- Multi-factor authentication (MFA), permission reviews, and prompt account removal when employees leave
- Email and web filtering, plus security awareness training for staff
No single tool covers every risk, which is why we use a layered approach to our cybersecurity services. Leadership gets clear reporting on what was found, what was done, and what still needs a decision.
The same discipline extends to Microsoft 365 and other cloud applications. Structured onboarding and offboarding keep access changes from stalling or leaving old accounts behind.
3. Predictable Budgeting
The real value of managed IT services is predictability. Unplanned emergency repairs and recovery work are hard to budget for. A consistent monthly structure makes it easier to plan hardware refresh cycles, Microsoft 365 licensing, and security improvements ahead of time.
Regular license and asset reviews also show where technology spending supports real work and where cleanup is needed. That turns IT from an unpredictable expense into a planned investment.
4. Expertise You Don’t Have To Hire
Few small and midsize organizations can employ full-time specialists in security, cloud infrastructure, networking, compliance, and business applications. A managed IT partner gives you access to that depth of knowledge through one relationship.
For organizations with short-term projects or specific skill gaps, IT staff augmentation adds experienced professionals without the time and cost of a full hiring process.
5. Stronger Compliance Readiness
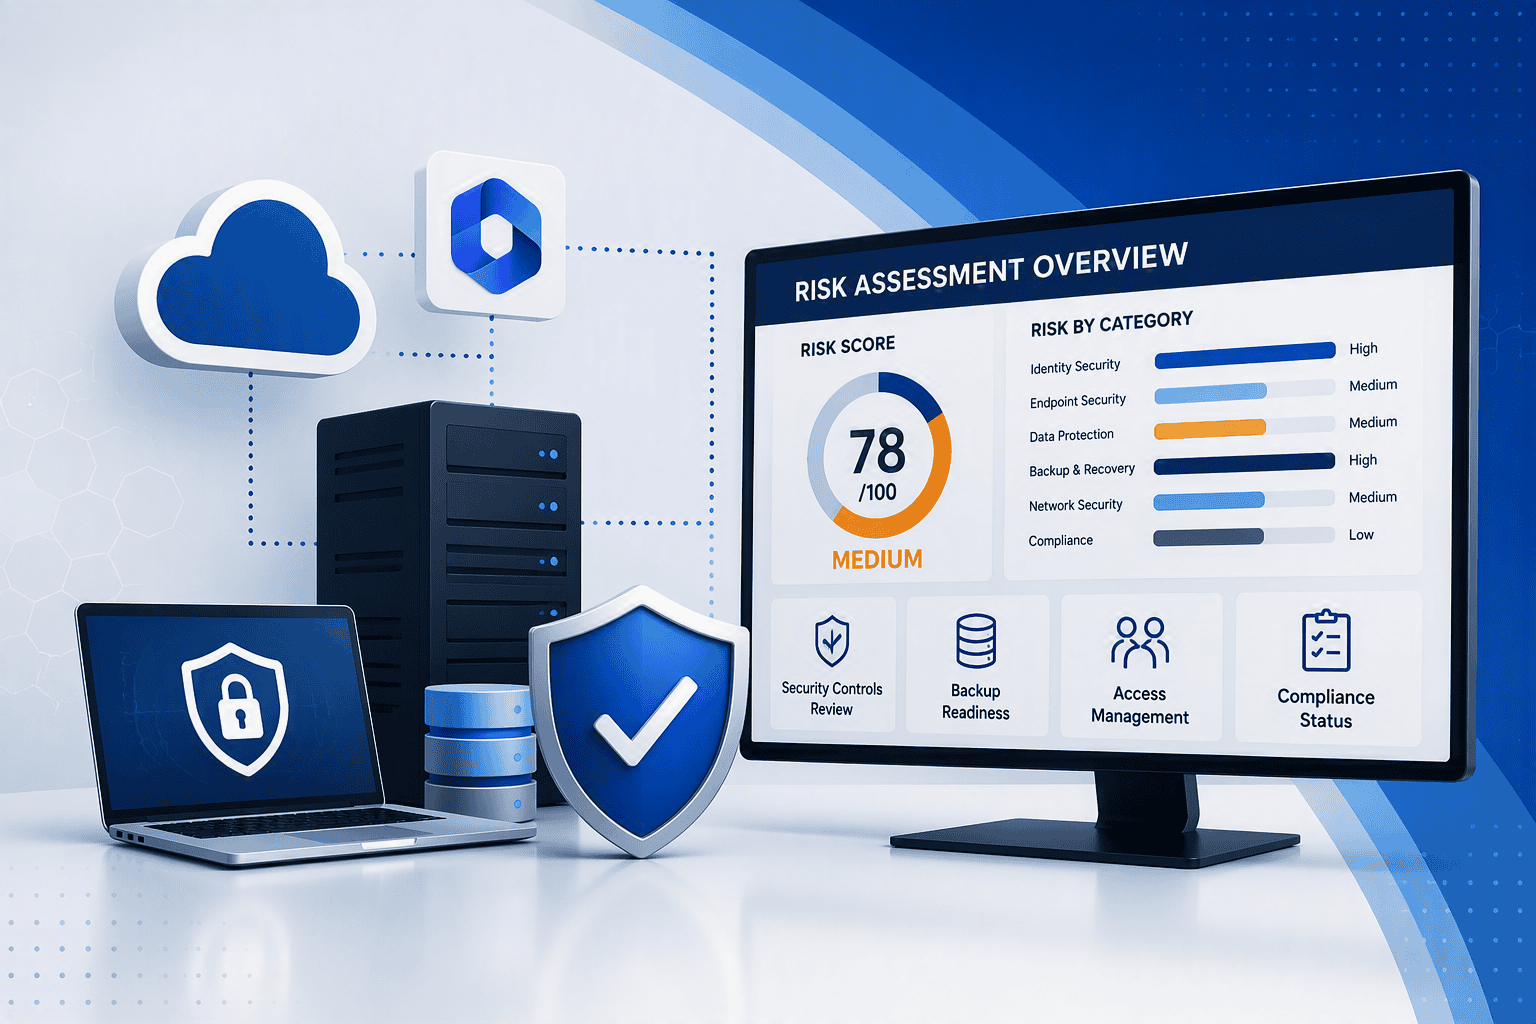
Regulated organizations need more than security controls. They need documented evidence of those controls, recorded risk decisions, and repeatable processes that auditors or cyber insurance carriers can review.
ACC’s approach incorporates the NIST (National Institute of Standards and Technology) Cybersecurity Framework and the CIS (Center for Internet Security) Controls. Through our Governance, Risk & Compliance (GRC) services, compliance readiness becomes part of ongoing risk management. A completed checklist is a benchmark, not a finish line.
6. Strategic Planning, Not Just Support
Day-to-day support keeps work moving. Strategic planning keeps technology aligned with your business’s direction. With true vCIO (virtual Chief Information Officer) services, leaders get technology roadmaps, quarterly business reviews, and budgeting support from someone who understands their goals.
That planning helps you decide when to upgrade systems, how to adopt new tools such as AI responsibly, and which risks to address first.
Not Sure How to Choose the Best MSP For Your Needs and Business Goals?
Read insider tips and learn exactly what you need to know to find an MSP that delivers exactly what your company needs.
For IT Leaders: How Managed Services Strengthen an Internal Team
If you already have internal IT staff, it doesn’t mean you have to hand everything off. Co-Managed IT Services add expertise and capacity where your team needs it, from extended monitoring coverage to complex infrastructure projects, while your staff keeps ownership of the environment they know best.
The value shows up in how you handle and document specific risk events. Here’s what that looks like in practice:
| Risk control area | Operational trigger | Managed service response | Evidence leadership can review |
| Endpoint isolation | A finance laptop shows suspicious activity after an invoice email is opened. | The SOC isolates the device, contains and remediates the threat, notifies ACC of the response, and restores access once the endpoint is clear. | Incident timeline, hostname, user, containment time, and endpoint status |
| Patch exception handling | A production SQL server can’t reboot during month-end close. | The deferral is documented, and an approved maintenance window is scheduled. | Patch report, exception ticket, business approval, and completion confirmation |
| Vulnerability prioritization | A scan flags a critical weakness on a public-facing VPN. | A security engineer validates the risk and tracks remediation. | Ranked findings, owner, due date, controls, and closure verification |
| Identity and access review | A former employee still has Microsoft 365 and CRM access. | The service desk disables the accounts and updates the offboarding checklist. | Access review, HR ticket, timestamp, and manager sign-off |
| Email and web threat control | Employees receive a credential-harvesting link. | The security team blocks the domain, searches mailboxes, and assigns follow-up training. | Quarantine logs, affected recipients, blocked URLs, and training records |
Mapping each response to NIST CSF 2.0 and CIS Controls v8.1 gives your team audit-ready evidence without adding to its reporting workload.
Whether you need fully managed or co-managed support, our guide to choosing a managed services provider covers the questions to ask before you decide.
A Partner That Takes Responsibility
Reliable IT shows up in ordinary moments: a finance lead closes invoices on time, a manager approves access without chasing three people, and a technician finds device history before a small ticket grows.
Most providers manage technology. ACC takes responsibility for it. Since 1991, we’ve supported nearly 250 businesses across Central and Upstate New York, and our clients stay with us an average of 12+ years because that ownership endures.
If you’re rethinking how your organization manages technology, book a meeting with our team to talk through your systems, security needs, compliance obligations, and growth plans.
Explore Expert Managed Services in Syracuse
Frequently Asked Questions
Can managed IT services work alongside an internal IT team?
Yes. Co-Managed IT Services add expertise, capacity, and specialized resources to an existing internal team rather than replacing it. Your staff keeps ownership of the environment they know best, while the managed partner fills skill gaps, extends coverage, or supports complex projects such as infrastructure upgrades and security programs.
Which industries benefit most from managed IT services?
Any organization that depends on technology can benefit, but the value is clearest where downtime, security, and compliance carry high stakes. That includes healthcare, financial services, insurance, legal, and professional services, as well as manufacturing, nonprofits, and local governments that need dependable systems for essential public services.
Are managed IT services worth it for small businesses?
For organizations with little or no internal IT staff, managed services provide expertise that would be difficult to hire individually. The value comes from fewer disruptions, stronger security, and planned technology spending rather than unplanned emergency repairs.
Do you provide managed IT services outside Syracuse?
Yes. ACC is headquartered in East Syracuse, New York, and supports organizations throughout Central and Upstate New York. Our team combines remote monitoring and support with on-site help when it’s needed. Our local team page has more on managed IT services in Syracuse and the surrounding region.